


Privileged Access Management Solutions Market Trends Highlight Cloud Automation and Governance
Changing PAM Priorities
The Privileged Access Management Solutions Market Trends reflect changing enterprise infrastructure and growing attention to identity-related security risks. Organizations are managing privileged access across cloud services, remote systems, endpoints, and automated applications. They are also seeking ways to reduce permanent permissions and improve visibility into administrative activity. Established controls such as credential vaulting remain important, but they are increasingly combined with access workflows and broader identity governance. Trends should be evaluated against actual operating needs. A new feature is valuable only if it reduces risk or improves efficiency without introducing unacceptable complexity.
Temporary and Least-Privilege Access
Organizations increasingly examine whether users need permanent administrative privileges. Temporary access can provide elevated permissions for a defined task or period, then remove them when no longer needed. Least privilege focuses on limiting access to the actions and resources required. These approaches can reduce exposure, but implementation requires reliable identity information, clear approvals, and practical emergency procedures. Some tasks still require persistent access or carefully managed exceptions. Teams should document those cases rather than assuming every privilege can be removed immediately. Measuring unused permissions and reviewing exceptions helps organizations refine policies over time.
Cloud and Machine Identities
Cloud environments create privileged roles for administrators, services, applications, and automated deployment tools. These identities can be created and changed quickly, making manual oversight difficult. Organizations are therefore paying closer attention to permissions, service accounts, and secrets used in automated workflows. Credential rotation and short-lived credentials can be useful where supported, but changes must be coordinated with application owners. Discovery is only the first step; teams also need to understand dependencies and assign responsibility. PAM may complement other cloud identity and security tools, but buyers should confirm how products share data and avoid conflicting policies.
Automation and Analytics
Automation can help discover accounts, rotate credentials, enforce approvals, and collect evidence for review. Analytics may help security teams identify unusual privileged activity or prioritize investigations. These capabilities can reduce repetitive work, but they depend on accurate data and sensible configuration. An automated rule that changes a service credential without understanding application dependencies can cause an outage. Likewise, alerts are useful only when teams can investigate them. Organizations should test automation in controlled stages and define ownership for exceptions. Human review remains important for high-impact decisions and for interpreting activity in its operational context.
Governance and User Experience
PAM adoption succeeds when security controls fit the way administrators and application teams work. Complicated approvals or unreliable access can encourage workarounds, undermining the purpose of the system. Organizations should involve users in policy design, provide clear training, and measure the time required to complete legitimate tasks. Governance should cover account ownership, periodic reviews, emergency access, and removal of unnecessary permissions. Security teams should also coordinate with procurement and vendor management when external providers require privileged access. The strongest trend is not a single technology feature, but the integration of privileged access controls into routine operations.
➤ In-Depth Market Studies by Market Research Future:
Architectural Rendering Software Market
Catégories
Lire la suite
Health-conscious consumers, mature retail networks and strong supplement habits define North America. Together they shape the Propolis Market across the region, where propolis reaches buyers through pharmacies, specialty stores and e-commerce. Imports from established beekeeping countries help supply this steady appetite. What Is Driving the Market? Natural wellness is the biggest driver....
The Baby Safety Products Market has become an increasingly relevant segment of the broader child-care industry as households place greater emphasis on preventive safety. Infants and toddlers interact with their surroundings differently from older children, often exploring objects through movement and touch. This creates the need for products that can help limit access to potentially dangerous...

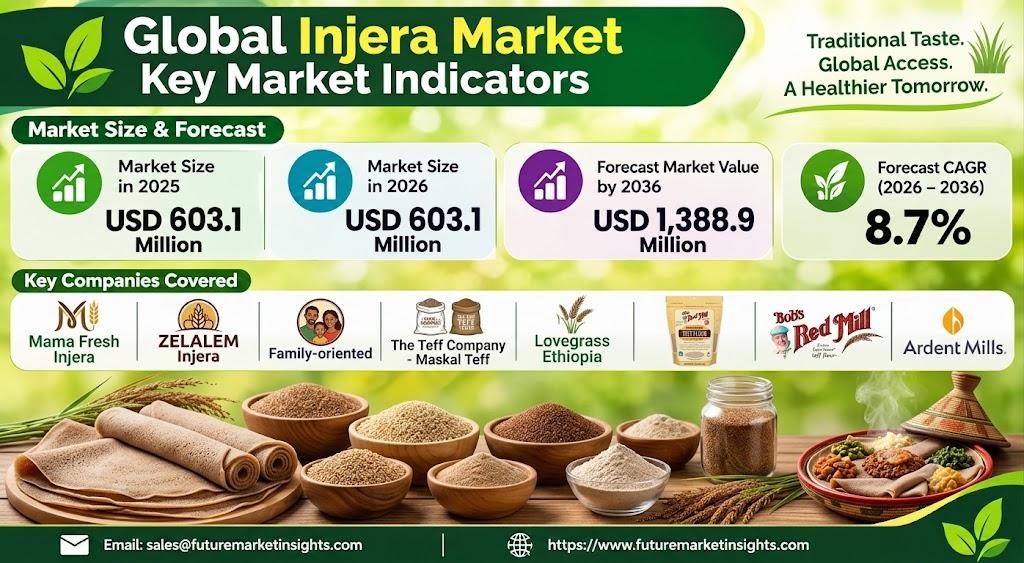
Injera Market Size to Reach USD 1.39 Billion by 2036, Growing at 8.7% CAGR, By FMI Report NEWARK, Del., October 29, 2026 — The global injera market is gaining momentum as demand for traditional fermented flatbreads expands across household consumption, ethnic food retail, restaurants, and commercial foodservice. Growing interest in Ethiopian and East African cuisine, together with wider...
Packaging has gradually become an important connection between products, transportation systems, and customer presentation. Across retail, manufacturing, warehousing, and logistics industries, businesses continue searching for packaging materials that support practical handling while maintaining organized appearance during storage and distribution. Wrapping Films from jtpackage are increasingly...

The RF hyperthermia machine market is evolving, driven by technological innovation, changing clinical practices, and the growing emphasis on combination therapies. These trends are not just reshaping device design—they are redefining how cancer and other conditions are treated. Analyzing these shifts provides a roadmap for understanding the future direction of the RF Hyperthermia...